Opens in a new tab
Open Nav
Sign Up

Urgent Security Alert: SQL Injection Vulnerability in WordPress Ultimate Member Plugin (CVE-2024-1071)

Bar Refael

February 26, 2024

A critical unauthenticated SQL Injection vulnerability, identified as CVE-2024-1071, has been discovered in versions 2.1.3 to 2.8.2 of the Ultimate Member WordPress plugin. This vulnerability affects over 200,000 active installations and allows attackers to inject malicious SQL commands through the ‘sorting’ parameter. Successful exploitation could lead to the extraction of sensitive information, including password hashes, from the database.

Vulnerability Details:

  • CVE ID: CVE-2024-1071
  • Affected Versions: Ultimate Member WordPress Plugin versions 2.1.3 to 2.8.2
  • Impact: SQL Injection, Data Exfiltration

Impact:

  • Unauthorized access to sensitive information
  • Potential compromise of user credentials and data
  • Risk of further exploitation and compromise of the affected WordPress sites

Recommendations:

  • Update: Immediately update the Ultimate Member plugin to version 2.8.3 to mitigate the vulnerability.
  • Review: Conduct a security review of your WordPress site to ensure no unauthorized access or changes have occurred.
  • Monitor: Monitor your website for any unusual activity or unauthorized access attempts.
  • Educate: Educate your website administrators and users about safe browsing practices and security measures.

Action Required:

Immediate action is required to update the Ultimate Member plugin to version 2.8.3 to protect your website from potential exploitation. Failure to update could result in unauthorized access to your website and compromise of sensitive information.
Stay Secure. Stay Informed.

OP Innovate Research Team.

Resources highlights

CVE-2026-109518 Bypasses APT Package Verification to Enable Root-Level RCE on Debian and Ubuntu

A high-severity vulnerability in the APT package manager could allow attackers to bypass package integrity verification and execute malicious code with root privileges on Debian,…

Read more >

CVE-2026-109518

Critical Rails Active Storage Flaw CVE-2026-122006 Enables Arbitrary File Writes Through Malicious Uploads

A critical vulnerability in Ruby on Rails could allow unauthenticated attackers to manipulate files on vulnerable application servers simply by uploading a specially crafted file.…

Read more >

cve-2026-122006_rails

Node2Shell (CVE-2026-111497) Under Active Exploitation as Critical Brotli Flaw Extends Beyond Node.js

A critical vulnerability in Google's Brotli decompression library is drawing increasing attention from attackers, with exploitation attempts observed just days after patches became available. Tracked…

Read more >

node2shell

PHP2Shell: Critical PHP RCE Flaws Targeted in Attacks (CVE-2026-109618 & CVE-2026-109619)

Attackers are targeting two critical vulnerabilities in PHP. The vulnerabilities, collectively known as PHP2Shell are tracked as CVE-2026-109618 and CVE-2026-109619, and could allow unauthenticated attackers…

Read more >

php2shell

ConnectWise SkyKick Compromise: Attackers Hijack Trusted Microsoft 365 Applications to Access Customer Tenants

A compromised application credential belonging to ConnectWise Cloud Backup, formerly known as SkyKick, has been used in a supply chain attack targeting Microsoft 365 environments.…

Read more >

skykick_op

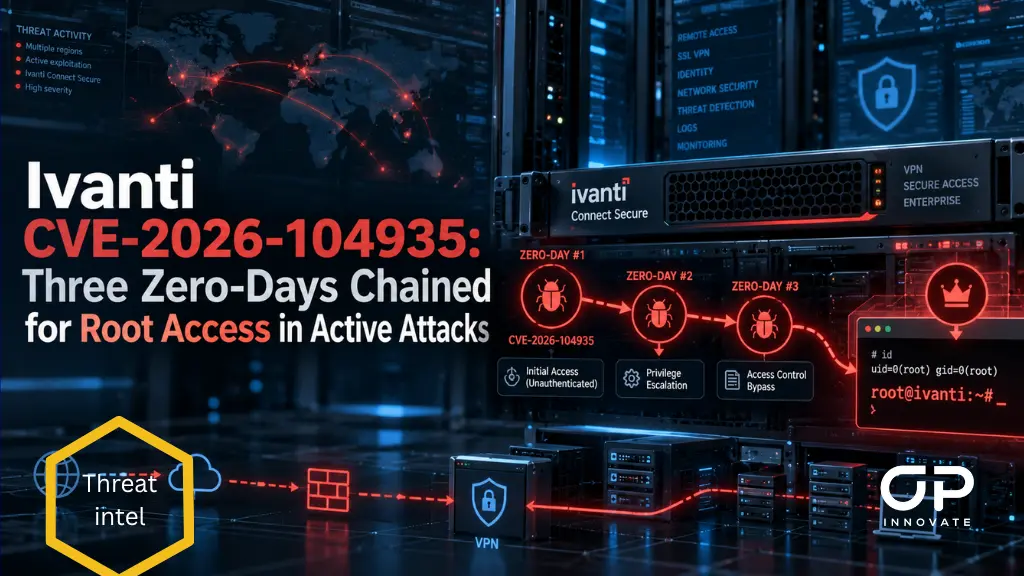
Ivanti CVE-2026-104935: Three Zero-Days Chained for Root Access in Active Attacks

Ivanti has released emergency security updates after attackers exploited a chain of three zero-day vulnerabilities in its Connect Secure VPN appliances to gain root-level access…

Read more >

ivanti_cve-2026-104935
Under Cyber Attack?

Fill out the form and we will contact you immediately.