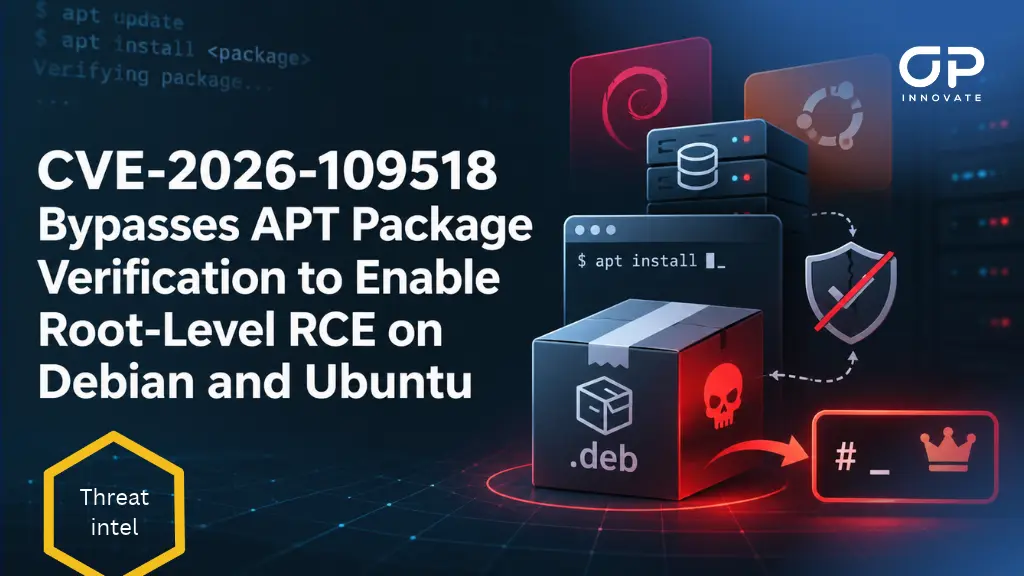
A high-severity vulnerability in the APT package manager could allow attackers to bypass package integrity verification and execute malicious code with root privileges on Debian, Ubuntu, and derivative Linux distributions.
Tracked as CVE-2026-109518, the vulnerability carries a CVSS 4.0 score of 7.7 (High) and was publicly disclosed on November 4, 2026. Discovered by security researcher Max Justicz, the flaw allows an attacker who can manipulate package-download traffic to replace legitimate software packages with malicious alternatives, potentially compromising affected Linux systems during routine software installations.
Both Debian and Canonical have released security updates addressing the vulnerability.
CVE-2026-109518 Overview
CVE-2026-109518 is a package verification bypass vulnerability involving improper handling of hard links during HTTP redirects and download retries.
The flaw affects APT’s HTTP backend and therefore extends beyond the apt command itself. Other applications relying on the same APT infrastructure, including apt-get, aptitude, and certain graphical package-management tools, may also be vulnerable.
Successful exploitation requires an attacker to control or manipulate HTTP traffic between the affected system and its package repository. Potential attack scenarios include compromised network infrastructure, malicious package mirrors, and attacker-controlled HTTP proxies.
The vulnerability also depends on APT’s Acquire::Retries configuration setting being greater than zero. This setting determines whether APT automatically retries unsuccessful package downloads.
A retry value of 3 is enabled by default in Debian 12 and later and Ubuntu 22.04 LTS and later, meaning these releases are vulnerable in their default configurations unless the relevant security patches have been installed.
Older distributions are not affected under their default retry configurations but may become vulnerable if administrators or automation scripts have explicitly enabled retries.
How Attackers Can Bypass APT Package Verification
APT normally protects software installations by validating downloaded packages against trusted repository metadata. These checks help ensure that installed packages have not been modified or replaced by unauthorized third parties.
CVE-2026-109518 undermines this protection by exploiting how APT handles file references across redirected and retried downloads.
According to the Debian security advisory, APT can incorrectly merge two separate package downloads when an HTTP redirect causes them to reference the same URI.
Improper handling of hard links during subsequent download retries can then allow an attacker to overwrite package contents after the original verification has taken place.
The attack involves several conditions:
- A vulnerable system initiates a package installation through APT using an HTTP repository.
- An attacker positioned along the communication path manipulates HTTP responses, including redirects and transient server errors that trigger download retries.
- APT incorrectly handles the resulting downloads and associated hard links, allowing attacker-controlled package contents to replace a previously verified file.
- The modified package is installed without the expected integrity checks being applied to its final contents.
The consequence is particularly severe because Debian packages can contain installation scripts that execute with root privileges.
By substituting a malicious .deb file, an attacker could potentially execute arbitrary commands with the highest level of privileges on the affected system.
The APT development team’s security announcement describes the underlying issue as a critical file verification bypass.
Importantly, the vulnerability does not allow arbitrary remote attackers to compromise Linux systems simply by connecting to an exposed network service. Exploitation depends on an actual package installation, a vulnerable retry configuration, and the ability to manipulate the relevant package-download traffic.
Affected Linux Distributions and Fixed Versions
The vulnerability affects multiple supported Debian and Ubuntu releases. Security updates are available for the following versions:
| Linux distribution | Fixed APT version |
| Debian 12 (Bookworm) | 2.6.2 |
| Debian 13 (Trixie) | 3.0.4 |
| Debian unstable (Sid) | 3.3.6 |
| Ubuntu 22.04 LTS | 2.4.15ubuntu0.1 |
| Ubuntu 24.04 LTS | 2.8.4ubuntu0.1 |
| Ubuntu 26.04 LTS | 3.2.1ubuntu0.1 |
| Ubuntu 26.10 | 3.3.3ubuntu0.1 |
As of November 5, Debian’s security tracker still identifies the testing distribution, Forky, as vulnerable at APT version 3.3.5.
Canonical has also published fixes for older Ubuntu releases through Ubuntu Pro and Expanded Security Maintenance, including Ubuntu 20.04 LTS, 18.04 LTS, 16.04 LTS, and 14.04 LTS.
Administrators can check the installed APT version using:
apt-cache policy apt
The output should be compared with the appropriate fixed package version in the official Debian Security Tracker or Ubuntu Security Notice USN-8996-1.
Software installation through Snap is not affected because Snap uses a separate package-management infrastructure.
Mitigation and Recommendations
Organizations using affected Debian and Ubuntu systems should prioritize updating APT to the fixed version for their respective distributions.
Canonical has also published temporary mitigations that can reduce exposure while security updates are being deployed.
1. Install the latest APT security updates
Upgrade affected systems using the appropriate vendor-supported packages.
Canonical recommends applying updates with automatic download retries disabled for the duration of the upgrade:
sudo apt update && sudo apt upgrade -o Acquire::Retries=0
Setting Acquire::Retries to zero prevents the retry behavior required for this vulnerability, providing protection during the update process.
2. Prefer HTTPS for APT repositories
Organizations should review their configured package repositories and replace HTTP URLs with HTTPS endpoints wherever supported.
HTTPS helps protect package-download traffic against network-based manipulation by attackers positioned between the client and repository.
However, HTTPS alone does not eliminate the risk associated with a malicious or compromised repository endpoint. Installing the fixed APT version remains essential.
3. Disable automatic retries temporarily
Where immediate patching is not possible, administrators can temporarily configure Acquire::Retries to zero.
This prevents the vulnerable retry behavior, although it may reduce reliability when package downloads experience transient network failures.
The configuration should be reviewed after remediation.
4. Review automated build and deployment environments
Organizations should identify vulnerable APT versions in container base images, CI/CD runners, cloud images, and automated provisioning systems.
Updating existing servers alone may not be sufficient if newly deployed infrastructure continues to use vulnerable package-management components.
5. Investigate potentially compromised systems
Where suspicious package installations or network manipulation are identified, security teams should conduct a broader compromise assessment.
Patching prevents future exploitation but does not automatically remove malicious software, persistence mechanisms, or other changes introduced through a previously compromised package installation.
Stay Safe. Stay Secure.
OP Innovate Research Team