Expanding our knowledge and innovating is at the core of what we do at OP Innovate. That’s why attending the RSA conference for the first time this year was a very proud and exciting moment for us.
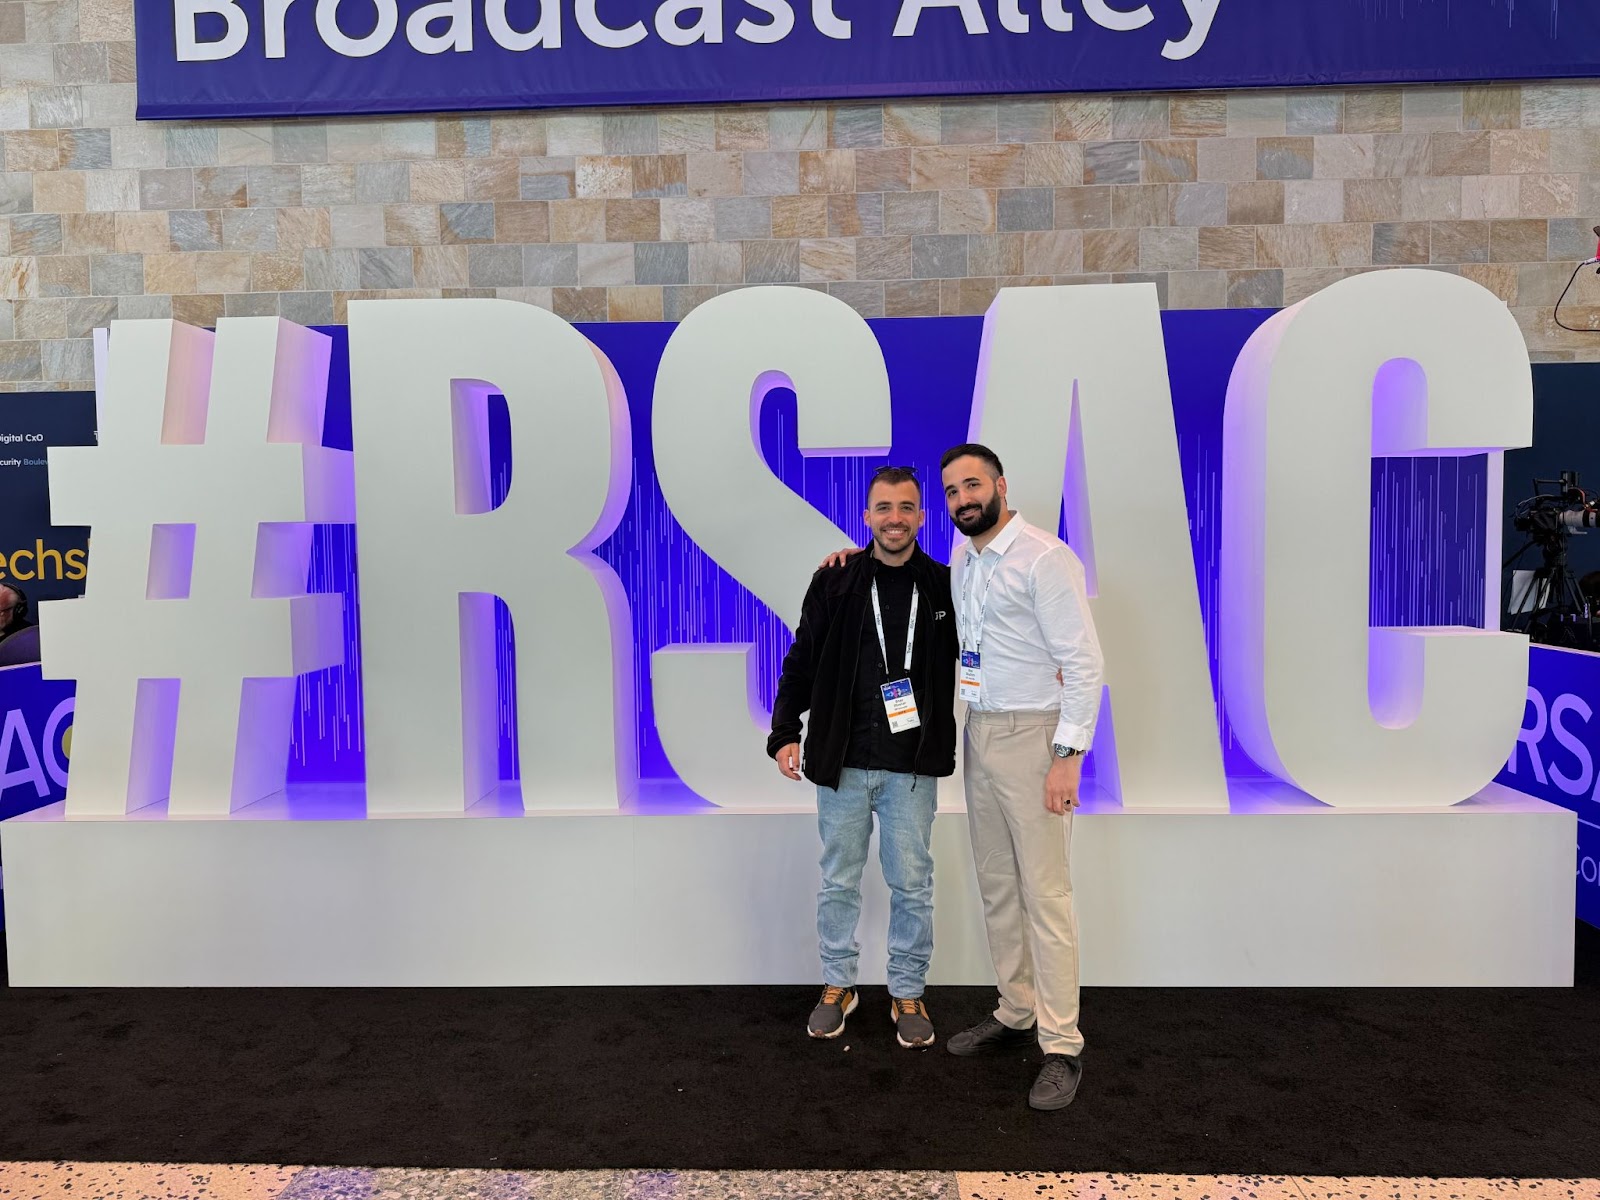
From April 28 to May 1st, Shay Pinsker (Chief Operating Officer) and Dan Shalom (Director of Research) were on the ground in San Francisco, rubbing shoulders with some of the brightest minds and leaders in cybersecurity.
With AI dominating headlines and global threats growing in complexity, we were happy to explore what’s next for the industry and how it aligns with the work we do every day.
AI Is Everywhere, but Execution Still Lags
As we expected, artificial intelligence was the dominant theme at RSA 2025. But even though nearly every vendor claimed some form of AI integration, only a handful demonstrated truly modular or dynamic AI decision-making in action. From what we’ve seen, there’s still a long way to go before AI reaches its full potential in cybersecurity.
There is a good and a bad side to this.
The good is that there is still a lot more that we as a company, and the industry as a whole, can build, refine, and innovate when it comes to applying AI in meaningful, security-first ways.
The bad is that threat actors are already leveraging AI to accelerate their attacks by automating phishing, evading detection, and exploiting misconfigurations faster than most defenses can keep up.
Where Continuous Pentesting Stands Apart
This growing gap between attacker innovation and defensive maturity is exactly why continuous validation and proactive testing are more critical than ever.
Interestingly, there weren’t many PTaaS (Penetration Testing as a Service) companies at RSA, at least not ones offering continuous, integrated testing like OP Innovate’s WASP platform. Some companies offered external attack surface management (ASM) capabilities, but from what we saw, they lacked the depth and real-world realism that manual testing brings.
This reaffirmed the need for platforms like WASP that combine automation with expert-driven offensive testing and real-time reporting, reducing mean time to remediation (MTTR) by up to 80%.
FIDO Keys and the Push Toward Phishing-Resistant MFA
Beyond the AI buzz, another trend we noticed at RSA 2025 was the growing interest in physical FIDO keys for multi-factor authentication (MFA). As credential-based attacks remain one of the most common and effective initial access methods, enterprises are beginning to phase out traditional passwords in favor of more phishing-resistant authentication.
We saw a noticeable increase in vendors offering hardware-backed solutions aimed at strengthening identity assurance and reducing the risk of compromised credentials. It’s a promising sign that secure identity is finally being treated as a critical part of the security stack.
What Everyone Was Talking About: Core Security Priorities
Several security domains consistently dominated the floor and breakout sessions at RSA 2025. The most talked-about challenges and product categories included:
- Security Operations Centers (SOC): Tools to improve visibility, triage, and incident response
- Software Composition Analysis (SCA) / Static Application Security Testing (SAST): Growing interest in securing the software supply chain
- Endpoint Detection & Response (EDR): Continued evolution of endpoint security with a push toward more behavioral detection
- Cloud Security: New tools and architectures to address misconfigurations, identity management, and workload protection in hybrid and multi-cloud environments
It’s clear that while innovation is happening, many organizations are still working to solidify the foundations of their security programs, which makes it even more important to continuously validate whether those investments are truly effective.
A Few Lighter Notes from the Floor
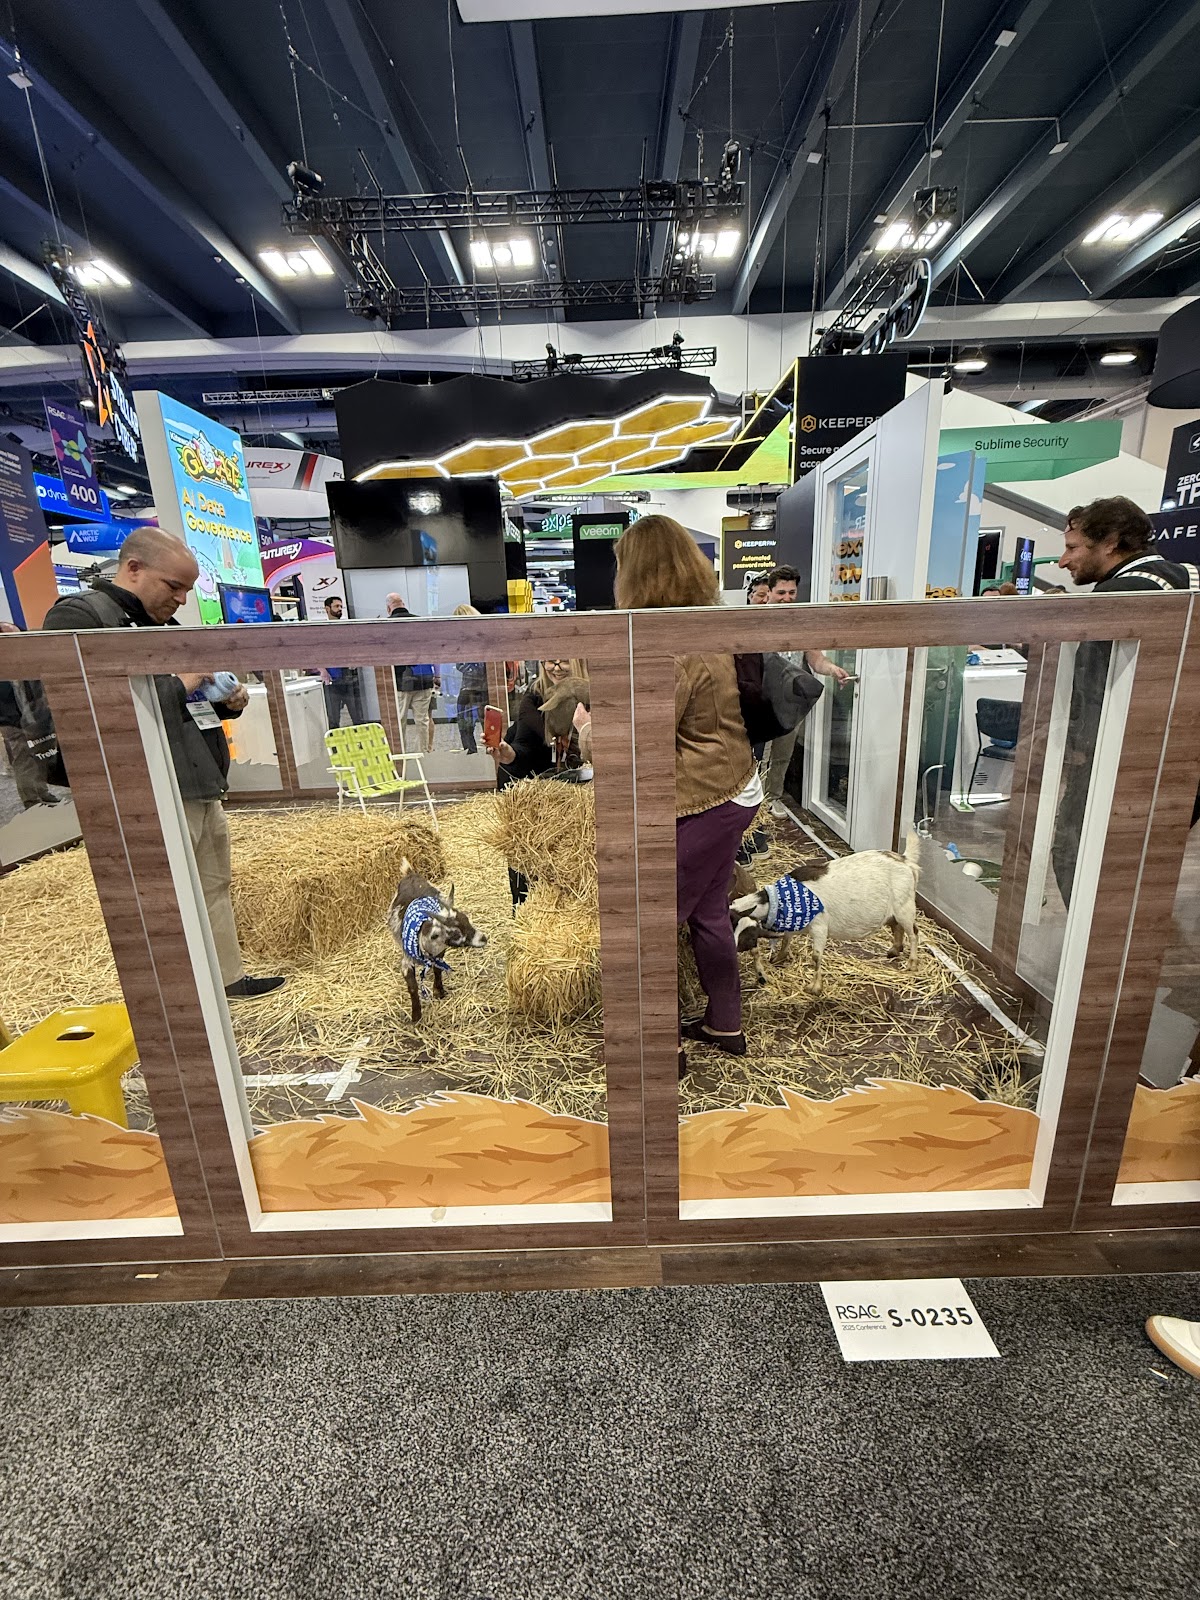
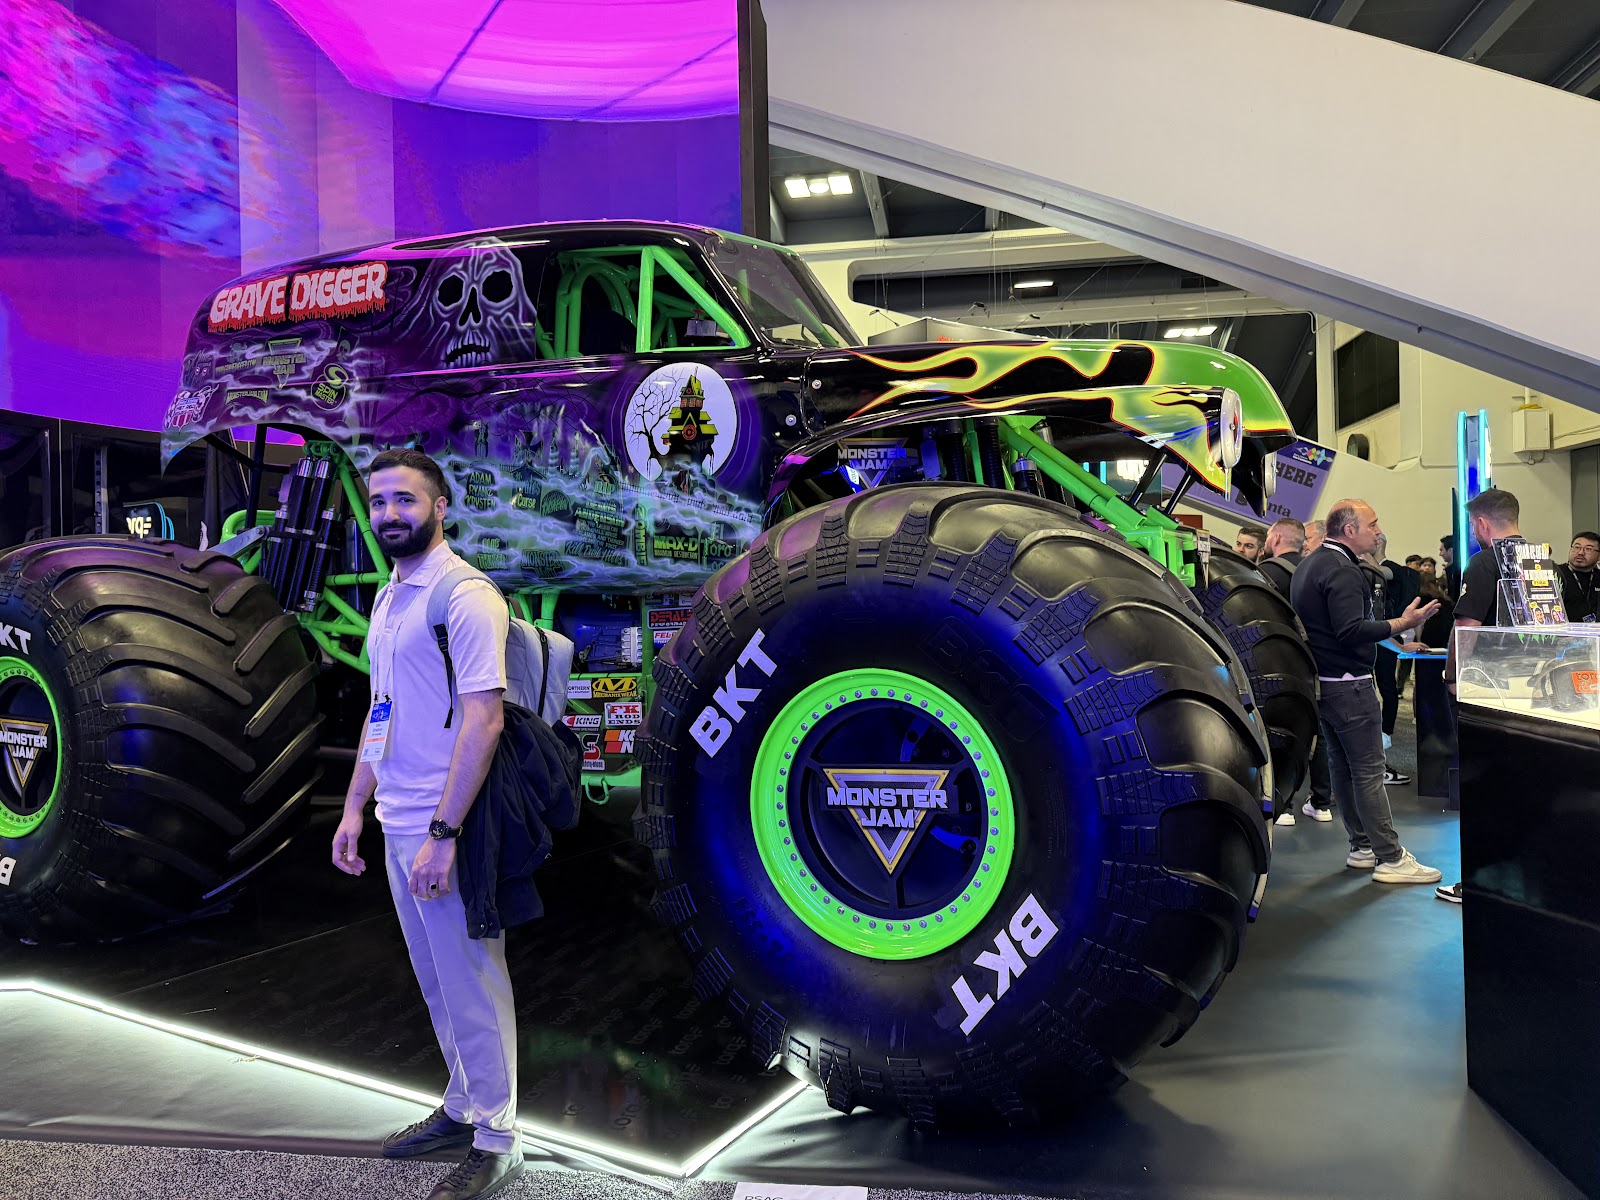
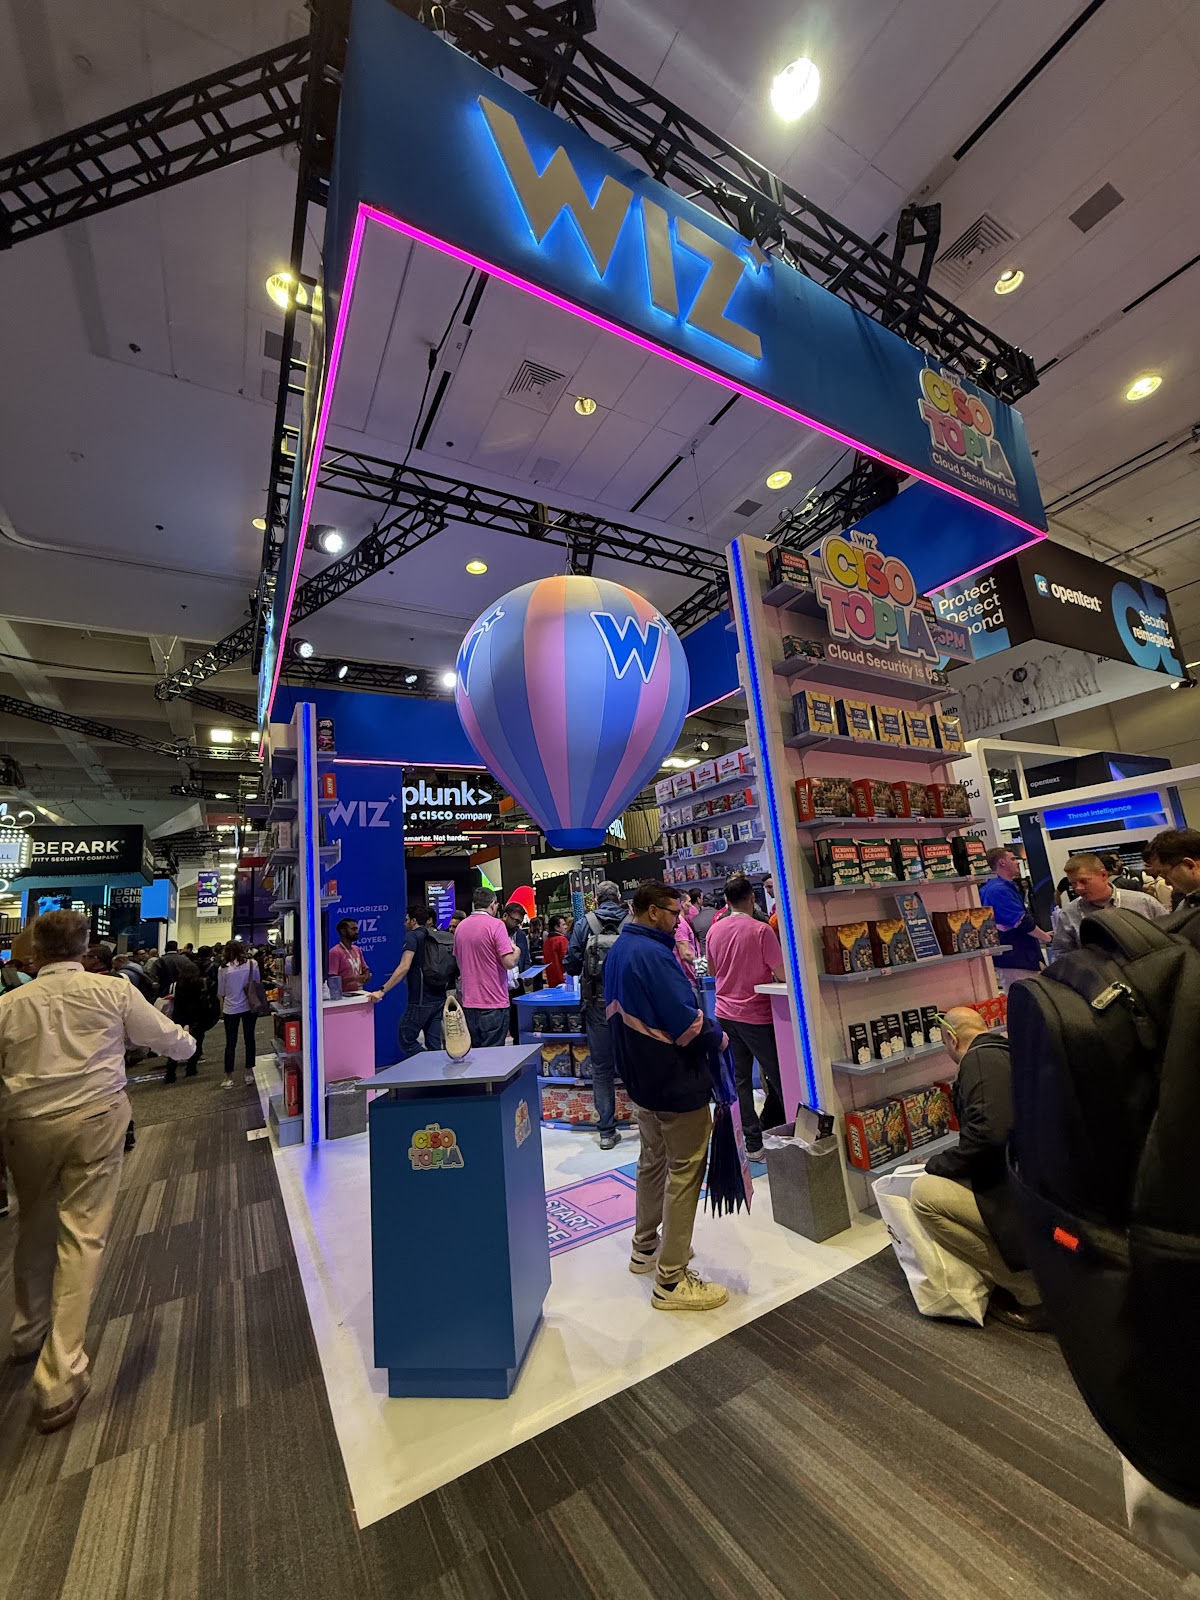
As much as we enjoyed diving into technical sessions and industry trends, RSA also has a lighter side to it. The competition to get as many eyes on your product as possible results in some eye-catching booths, live demos, and clever ways to draw in the crowd.
It reminded us that while cybersecurity is serious business, there’s still room for energy and a little fun. Here are some of the most creative booth moments we came across (yes, someone literally brought in goats inside the building):
Final Thoughts: Security Shouldn’t Wait
We came to RSA 2025 looking for insight, and left even more confident in our mission. We believe that proactive security and continuous validation aren’t just future goals; they’re essential for today’s threats.
While some vendors are just starting to explore continuous security, OP Innovate has long been delivering it. WASP brings together automated scanning and expert-led validation to help organizations reduce risk in real time, not just once a quarter (or year).
Want to learn how WASP can help you get ahead of AI-driven threats?
Contact us for a live demo or sign up for FREE to get started today.