Vulnerability Summary:
- Affected Software: Atlassian Confluence Data Center and Server.
- Type of Vulnerability: Remote Code Execution (RCE).
- Exploitation Status: Actively exploited by hackers.
- CVE IDs: CVE-2023-22522 and CVE-2023-22527 (CVSS score: 10.0).
Context and Recent Developments:
Two critical vulnerabilities in Atlassian Confluence software, CVE-2023-22522 and the newly disclosed CVE-2023-22527, are currently under active exploitation by hackers. These RCE flaws allow attackers to execute arbitrary code on the server hosting Confluence, leading to potential full system compromise.
Notably, CVE-2023-22527 affects versions of Confluence Data Center and Server released before December 5, 2023, and version 8.4.5. Within just three days of this vulnerability’s public disclosure, nearly 40,000 exploitation attempts have been recorded, originating from over 600 unique IP addresses globally.
Expanded Implications:
- Geographical Distribution of Attacks: The majority of attack attempts are originating from Russia, followed by Singapore, Hong Kong, the U.S., and other countries.
- Internet-Exposed Instances: Over 11,000 Atlassian instances are internet-accessible as of January 21, 2024, with an unknown number vulnerable to CVE-2023-22527.
- Nature of Exploitation: Early activities include testing callbacks and executing ‘whoami’ commands, indicating preparatory steps for more extensive exploitation.
Stacked Area Chart of Atlassian Confluence Exploitation Attempts by Region
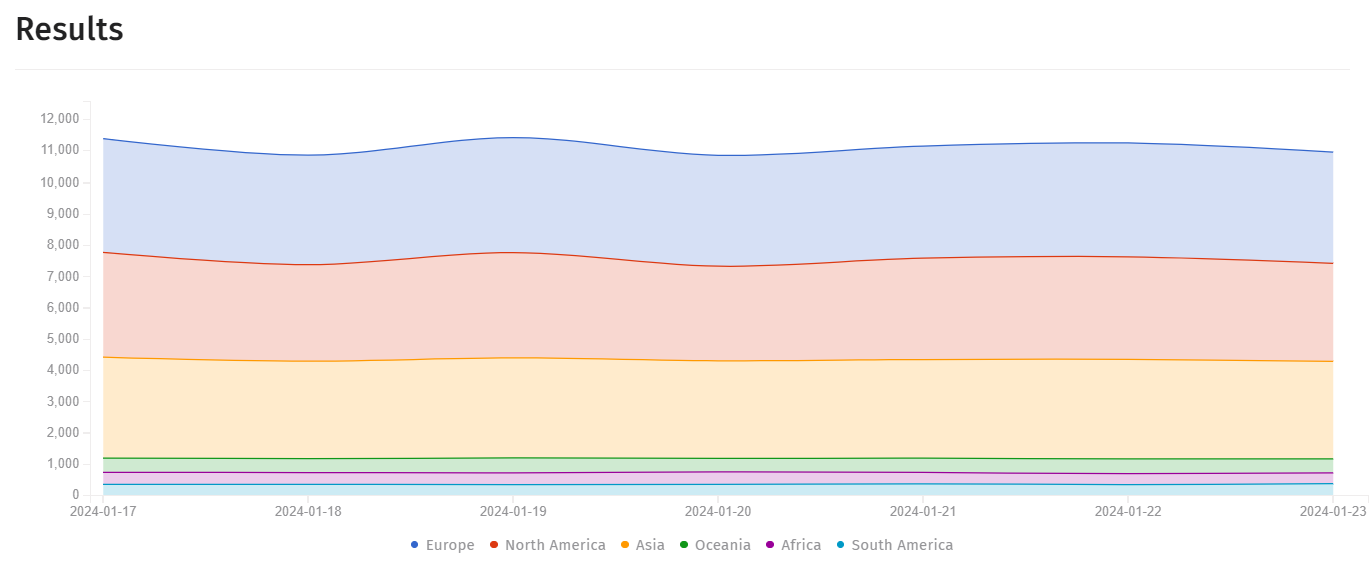
Figure 1: This chart visualizes the frequency of exploitation attempts on Atlassian Confluence software over a one-week period, segmented by global regions. Europe and North America are depicted as having the highest levels of activity, with Asia, Oceania, Africa, and South America following. Data sourced from the Shadowserver Dashboard.
Response and Mitigation:
- Immediate Patching: Update all Atlassian Confluence Data Center and Server installations to the latest secure versions immediately.
- Enhanced Network Monitoring: Intensify surveillance for signs of exploitation attempts, especially from the geographical regions with high attack instances.
- Vulnerability Assessment: Assess your Confluence installations for susceptibility to CVE-2023-22522 and CVE-2023-22527.
- Backup and Recovery: Verify that all critical data is backed up and that recovery plans are current and operational.
Recommendations for OP Innovate Clients:
- Review and Update: Ensure your Atlassian Confluence installations are not among the outdated, vulnerable versions.
- Security Awareness and Training: Educate your teams about these vulnerabilities and the importance of vigilance in detecting suspicious activities.
- Collaboration and Reporting: Coordinate closely with IT and cybersecurity teams to monitor, report, and respond to any potential security incidents.
Closing Note:
With the dramatic increase in exploitation attempts of these critical vulnerabilities, it’s imperative for organizations using Atlassian Confluence to take immediate action to protect their systems. OP Innovate is dedicated to providing the latest intelligence, support, and guidance to navigate through this evolving cybersecurity challenge.
Stay Safe and Informed,
OP Innovate.